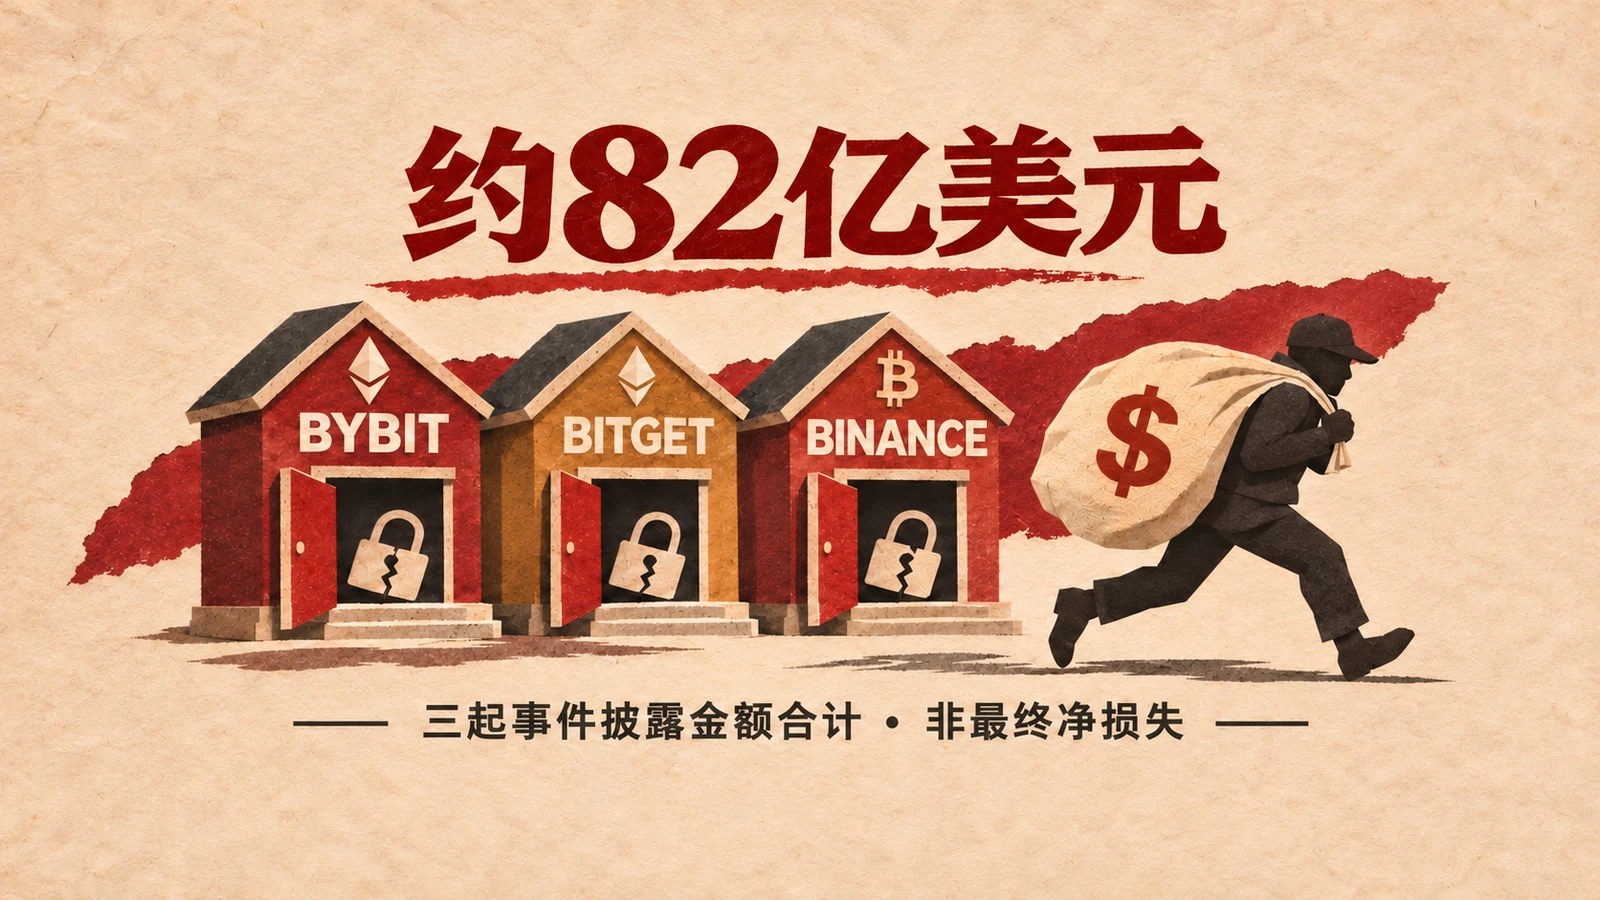
Three exchanges, three security incidents, and about $8.1875 billion in disclosed amounts. The headline number is arresting. The harder question is what happens after assets leave an exchange: which legal entity owes customers, what resources can fill the hole, and where can a customer enforce that claim? One platform may keep balances intact within days. Another may leave creditors waiting through years of rehabilitation. Technology alone does not explain the difference.
Put the three figures on the table
In February 2025, attackers removed about $1.46 billion in Ethereum-related assets from one Bybit cold wallet. Bybit subsequently said it had restored 1:1 reserve coverage for the relevant customer assets within 72 hours and published a third-party reserve check. That illustrates the ability of a large platform to mobilise liquidity and resources quickly. It does not mean the stolen assets were recovered, or that a larger future incident would end the same way.
In September 2026, Bitget reported approximately $387.5 million transferred to attacker-controlled addresses, above its initial estimate. The exchange later said customer account balances were unchanged and that its Protection Fund had been replenished to more than $300 million. Those claims and the fund deserve scrutiny. A $300 million fund headline is not the same thing as an immediately enforceable, unlimited right to compensation for every possible loss.
In October 2026, Binance said a severe security incident affected approximately $6.34 billion in virtual assets. Its preliminary report said about $2.85 billion had been frozen or intercepted as of 3 November. The US Federal Bureau of Investigation described more than $6 billion as stolen and attributed the attack; that is not a final account of each customer's net loss. Binance said on 4 November that it had used its own resources to replenish about 98% of the affected tokens while withdrawals reopened in stages. This is the company's reported progress, not independent proof that every customer has received a completed payout.
Adding $1.46 billion, $387.5 million and $6.34 billion gives $8.1875 billion, rounded to roughly $8.2 billion in the headline. The three disclosures do not use identical accounting: transferred, affected, frozen, replenished and final net loss are different things. Even after recoveries, the scale forces a sharper question than “is this exchange secure?” If the gap exceeds the capital it can mobilise, who writes the final cheque?
Mt. Gox: wanting to pay is not the same as being able to pay
In 2014, Mt. Gox reported roughly 850,000 bitcoin missing—about 750,000 corresponding to customers and about 100,000 belonging to the company. It later found around 200,000 bitcoin in an old wallet. The rest did not reappear when trading stopped. The exchange entered legal proceedings, and creditor verification, asset disposition and repayment have stretched across years. Its rehabilitation site now lists 31 October 2027 as the deadline for certain repayments.
This cannot be reduced to a slogan about a platform's goodwill. If missing assets exceed what a company has or can raise, management cannot create the shortfall with a press release. A customer who thought they held withdrawable coins instead holds a claim governed by the available asset pool, priority rules, courts and time. That is the brutal conversion in centralised custody: identical balances on a screen can become very different enforceable rights when the custodian fails.
Bitfinex supplies a different historical path. After a 2016 bitcoin theft, it initially applied a 36.067% generalised loss to accounts and issued BFX tokens to record customer claims. In 2017 it said those tokens had been redeemed or converted into equity. The eventual outcome does not erase the first decision: the platform proposed who would bear the gap and in what form people would wait for compensation. Later repayment was a business and financing outcome, not a rule every customer of every exchange can rely on.
The two gates that decide a customer's fate
The first is capacity to pay. A proof-of-reserves snapshot may show coverage of specified assets at a specified moment. It does not automatically expose every group liability, liquidation constraints, related-party exposure or who absorbs the next extreme loss. Insurance, protection funds and “1:1 reserves” each have their own scope, conditions and responsible entity. The fact that one large platform can close today's hole does not establish that the industry can survive a still larger one. Treating “a big exchange will pay” as a safety system is a wager that it will always remain big and liquid.
The second is enforceable responsibility. Large exchanges serve customers across borders. The brand on an app, the contracting company, licensed entity, wallet custodian and group treasury may sit in different jurisdictions. Some activities are substantively supervised; others rely on offshore licences or permissions limited to a particular service. It is wrong to say all major exchanges are unregulated. It is equally wrong to assume a licence shown in a website footer gives every customer the same segregation, capital and insolvency protection. In a crisis the practical questions are simple: Which company signed my contract? Who holds the assets? Which supervisor can compel that company? Where can I sue, and what assets would a judgment reach?
In its 2025 peer review, the Financial Stability Board identified significant gaps and inconsistencies in implementation of crypto-asset regulatory recommendations and called for stronger cross-border cooperation. IOSCO's earlier recommendations addressed segregation, reconciliation, independent assurance and safe custody of client assets. The principles exist. The difficult work is making every operating entity, customer claim and asset path of a cross-border platform auditable and legally enforceable. An offshore licence that looks impressive in a footer but does not reach global custody or compensation is decoration, not a defence.
TraderVote view: customer protection cannot rest on a founder's reputation
Bybit's and Binance's reported use of their own resources, and Bitget's Protection Fund, are constructive responses that need continuing verification. But a customer's basic rights should not depend on whether a founder chooses to write a cheque, whether markets will refinance the exchange, or whether a scarce token can be bought back in time. Reputation can help a firm survive. It cannot replace pre-agreed liability, demonstrably available loss-absorbing resources and a cross-border resolution process that actually works when the firm does not survive.
Any exchange asking customers to trust it with their coins should make four things answerable without guesswork: who the contracting and custody entities are; whether client assets are segregated and independently reconciled; which verifiable capital or protection arrangements absorb an extreme shortfall; and where, in what order and through which process customers recover assets after a shutdown or insolvency. Without those answers, “your funds are safe” is an advertising line that may prove unenforceable precisely when it matters.
The industry's deepest systemic vulnerability is not that attackers will always exist; every financial infrastructure faces attacks. It is that platforms hold vast assets for a global clientele while customer protection may still depend on each platform's own promise. When the next massive theft occurs, customers should not have to rely on luck to learn whether their balances return in 72 hours or their claims remain unresolved a decade later.
Primary sources
- [Bybit incident timeline, 3 March 2025](https://www.bybit.com/en/learn/this-week-in-bybit/bybit-security-incident-timeline); [Bybit/Hacken reserve announcement, 24 February 2025](https://www.bybit.com/en/press/post/fully-backed-within-72-hours-bybit-maintains-1-1-customer-assets-ratio-in-latest-proof-of-reserves-audited-report-by-hacken-bltb767a9461133831f).
- [Bitget incident tracing update, 25 September 2026](https://www.bitget.com/support/articles/12560603896108); [Bitget Protection Fund update, 30 September 2026](https://www.bitget.com/support/articles/12560603896390).
- [Binance preliminary incident report, 3 November 2026](https://www.binance.com/en/square/post/384328127385979); [Binance recovery update #7, 4 November 2026](https://www.binance.com/en-GB/support/announcement/security-incident-recovery-update-7-98-of-stolen-assets-replenished-and-new-por-snapshot-with-expanded-coverage-2026-11-04-c6ba9aa726974fc6b9332a2c8f63b405); [US FBI alert, 31 October 2026](https://www.fbi.gov/investigate/cyber/alerts/2026/north-korea-responsible-for-6-billion-binance-attack).
- [Mt. Gox announcement, 20 March 2014](https://www.mtgox.com/img/pdf/20140320-btc-announce.pdf) and [rehabilitation site](https://www.mtgox.com/); [Bitfinex loss-allocation notice, 6 August 2016](https://blog.bitfinex.com/announcements/bitfinex-interim-update/) and [BFX redemption notice, 3 April 2017](https://blog.bitfinex.com/announcements/100-redemption-outstanding-bfx-tokens/).
- [Financial Stability Board peer-review summary, 16 October 2025](https://www.fsb.org/2025/10/fsb-finds-significant-gaps-and-inconsistencies-in-implementation-of-crypto-and-stablecoin-recommendations/); [IOSCO crypto-asset market recommendations, 2023](https://www.iosco.org/library/pubdocs/pdf/IOSCOPD734.pdf).
Sources checked on 6 November 2026, Los Angeles time. The cover is a conceptual illustration, not a photograph of an incident; its figure does not represent an identified suspect or imply the same perpetrator in all three cases. This article is not investment advice.
Discussion
Comments (0)
Sign in to join the discussion.
Sign inNo published comments yet. Start the discussion.